The AV/IT Industry Is Sleepwalking Into EU AI Act Compliance Risk.
Most AV/IT teams still think the EU AI Act is “an IT problem but It isn’t. It’s an AV problem, a workplace problem, and a human‑experience problem.
AV/IT Specialist, Experian
Benedict Onodu is an AV/IT Specialist at Experian and a recognised authority at the intersection of professional AV and cybersecurity. A Certified Technology Specialist (CTS), ISO 27001 ISMS Practitioner, and CompTIA-certified professional, Benedict brings a rare dual-domain expertise that helps organisations unify technical innovation with robust governance.
Benedict is passionate about mainstreaming cybersecurity and GRC for the Pro AV industry and advocates for integrated information security strategies tailored to creative and integrated experience environments. His commitment lies in driving operational resilience, regulatory alignment, and secure-by-design practices across the rapidly evolving digital and AV landscapes.
The AV/IT Industry Is Sleepwalking Into EU AI Act Compliance Risk.
Most AV/IT teams still think the EU AI Act is “an IT problem but It isn’t. It’s an AV problem, a workplace problem, and a human‑experience problem.
The Autonomous Workplace Threat Surface: AI Agents Are Now Exploiting AV & IT Systems.
AI agents aren’t just answering prompts anymore. They’re acting inside organisations. Enterprise platforms now give agents the ability to schedule meetings, trigger workflows, access APIs, update systems, and operate across AV & IT environments.
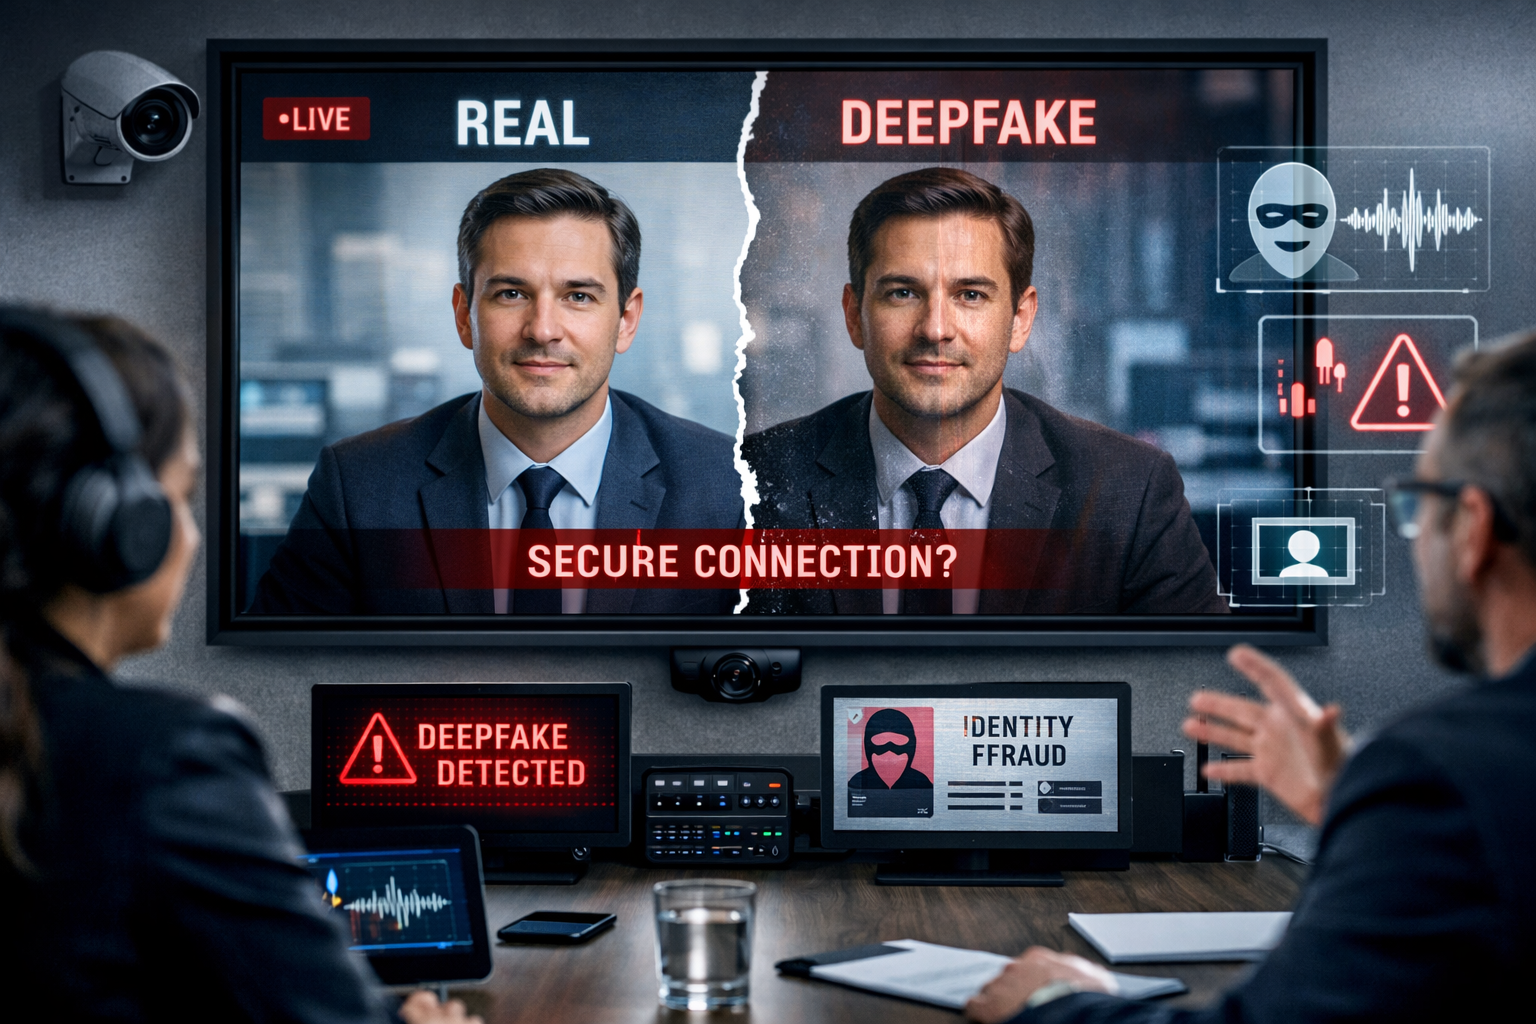
Deepfakes Are Now an AV Problem, the Industry Must Step Up.
Deepfakes have moved from online curiosity to operational threat. In the last two years alone, deepfake incidents have surged by 3,000%, with attackers now using AI‑generated video and voice to infiltrate meetings, impersonate executives, and manipulate live content streams.
AV/IT Is Officially Inside the EU AI Act Compliance Window; Here’s What That Really Means.
EU AI Act enforcement is already active: it took effect in August 2024. GPAI rules apply from August 2025, high‑risk obligations roll out through 2026, and full enforcement lands by August 2027, meaning AV/IT is already inside the compliance window.
Why AV Manufacturers Need to Pay Attention to the OWASP LLM Top 10
OWASP should be the backbone of secure LLM adoption in AV. If AV wants safer AI‑powered features, OWASP must sit at the core.
Designing AI‑Enabled AV Products with Governance in Mind.
The AI‑in‑AV market is projected to reach $28.6B by 2030, growing at 32% Compound Annual Growth Rate. At the same time, the UK AI sector grew 68% in revenue in a single year, signalling that enterprise buyers are scaling AI adoption, and they expect governance maturity from every vendor.
AI Is Already in Your Meeting Rooms. Governance Isn’t.
If you’re an AV manufacturer, integrator, or enterprise leader, here’s the truth: Your meeting rooms have quietly become AI‑powered decision engines capable of summarising, analysing, nudging, and influencing outcomes in real time but governance hasnt quite caught up, it’s miles behind.
Deepfakes Are Now an AV Problem and the AV Industry Must Take Responsibility.
Deepfakes aren’t just an IT or cybersecurity threat anymore. They’re entering meeting rooms, collaboration platforms, digital signage, broadcast systems, and AV‑over‑IP networks. If AV manufacturers and integrators don’t address this now, we’ll be reacting to a crisis later.
The Rise of AI in AV: Governance Is Now the Real Concern
AI is scaling rapidly across the AV industry, but governance isn’t keeping pace. And that gap is where the real risk sits.
When Screens Watch Back: What AV Manufacturers Must Get Right About AI‑Enabled Digital Signage
Digital signage has moved far beyond traditional displays. For manufacturers, the category is shifting into intelligent, sensor‑driven systems capable of observing, analysing, and reacting to their environment. This presents a different kind of risk.
AI Governance for AV Manufacturers: Why Label Governance MattersReal Change, Start with Label Governance.
AI transformation in the AV industry isn’t just about embedding new intelligent features — it’s about ensuring those features behave reliably, responsibly, and consistently across every customer environment.
How a Boardroom Mic can Become a Breach Vector
In today’s hyper-connected enterprise environments, the humble boardroom microphone, once just a tool for better audio, can quietly evolve into a potential cybersecurity threat.
Turning ISO 27001 Compliance into AV Business Value
Many AV companies still treat information security as an afterthought instead of a business enabler. ISO 27001 compliance isn't just about ticking a regulatory checkbox—it’s about unlocking competitive advantages, building trust, and ensuring operational efficiency in a rapidly evolving industry.
Navigating TPRM Compliance: Key Standards for AV Organisations
Third-Party Risk Management (TPRM) compliance is key for AV organisations to meet client expectations in today's data-driven environment. Adhering to standards like ISO 27001, SOC 2, NIST, GDPR, and DORA addresses critical risks, builds trust, and positions businesses as relaible partners.
DORA is live, Your customers are complying, should you?
The EU Digital Operational Resilience Act (DORA) regulaion took effect from 17th January 2025 with various localised adaptation in the work, Pro AV's passivity towards enterpr end-users Information Security risk priorities would no longer cut-it.
Under-prioritising Availability is not good for business.
The Confidentiality, Integrity and the Availability of information and data assets the pillars of Information Security. But the reality is most cybersecurity efforts prioritise the first two legs of the tripods and don’t pay much attention system Availability and user experience.